Casino Secrets methods raise serious hacking and privacy concerns
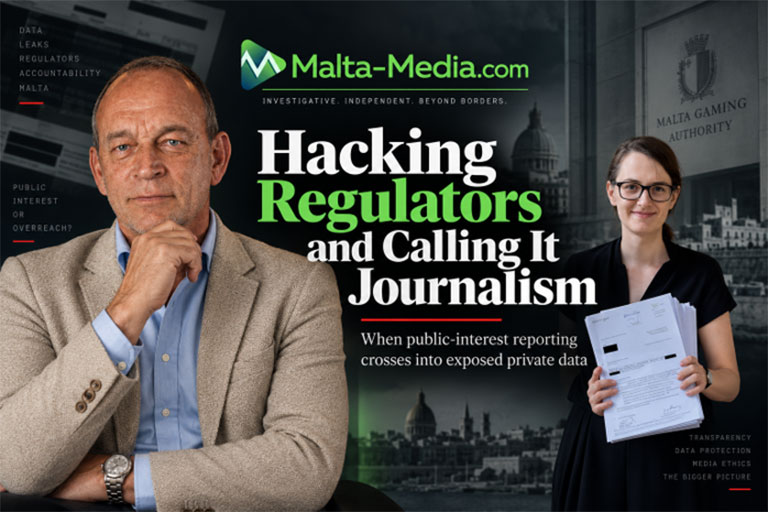
The Casino Secrets investigations have surfaced useful corporate questions around SoftSwiss, PlatinCasino, Lottoland and the Curaçao Gaming Authority. The problem, as described in the source text, is not the subject matter; it is the method used to obtain regulatory material and the way private data was handled afterward.
- The author says they have no issue with reporting on gambling companies hiding ownership, misleading regulators, avoiding tax, or operating unlawfully. The objection is narrower: whether the reporting remains sound when the underlying material comes from prolonged access to a regulator’s system rather than from a conventional whistleblower leak.
- In relation to the MGA incident, Lilith Wittmann publicly said, “Yes, I hacked you”, and her own Curaçao account says access to the CGA environment continued for approximately nine months. The text argues that this is not something to sanitize by calling it a standard leak.
- The distinction matters because regulator files are not just corporate ownership records. They can contain passports, dates of birth, residential addresses, source-of-funds material, employment records, proof-of-address documents, and information belonging to compliance staff, AML professionals, consultants, and employees who may never have been accused of anything.
- The source text says public interest can justify exposing ownership or wrongdoing, but it does not automatically justify exposing every private field sitting next to that evidence. That is the privacy problem high-risk operators and their PSPs should care about: once a regulator’s archive is breached, the collateral data set is much larger than the headline allegation.
- The text also notes that the MGA case should have triggered a wider discussion about this distinction. On 17 March 2026, the Malta Gaming Authority confirmed a one-line opening whose substance is cut off in the source provided, so the article cannot responsibly fill in the missing detail.
For PSPs, acquirers and compliance teams in high-risk verticals, the practical takeaway is simple: a leak is one thing, access to a regulator’s environment is another. If a case turns on hacked regulatory files, the privacy exposure extends far beyond the operator named in the story.
Related news
All news →
Winning Poker Network Makes ScreenShield the Default on Americas Cardroom From November 4
Bitget adds Kazakhstan, Russia, and Belarus to its restricted countries list
Brazil’s sudden betting ban puts more than R$ 9 billion in federal tax revenue, R$ 30 million licence fees, and billions in sponsorship contracts back in play
Weekly high-risk digest
Regulation, sanctions and payment news across your verticals — once a week, free.
Please check your inbox and click the link to confirm your subscription.
Please enter a valid email address!