New QR Code Pix fraud is diverting online shopping payments in Brazil
Kaspersky says it has identified 90 small and medium-sized online stores in Brazil infected with malicious code that swaps the original Pix QR Code at checkout for a fraudulent one. For PSPs and merchants, the important detail is not the malware itself but the payment-flow breakage: the store thinks the order is unpaid, while the money is quietly routed elsewhere.
- The fraud has been active since June 2025 and was recently discovered by independent security researcher “eremit4,” according to Kaspersky. Affected stores span several sectors, including optics, auto parts, fashion, and virtual fundraising platforms, with one common factor: they all use Magento.
- Attackers use six command-and-control domains to inject malicious code into checkout pages. When a customer chooses Pix, the code instantly replaces the merchant-generated QR Code, and also changes the “copy and paste” payment data, so both the visual and text-based payment paths are hijacked.
- Kaspersky says the fraud is quiet by design. On the merchant side, the order shows up as “abandoned” or pending because the store’s own system never registers the payment. On the customer side, the theft often becomes visible only days later, when the buyer contacts the store about a delayed delivery.
- That delay gives criminals enough time to spread the stolen funds across multiple mule accounts, which makes recovery harder. Fabio Assolini, Kaspersky’s lead security researcher, said the attack has strong potential for wider spread and warned that mobile shoppers are also exposed because many e-commerces offer copy-and-paste Pix payment flow.
- Assolini also pointed to Pix Automático and Pix Parcelado as expanding the attack surface, since both can work through QR Code reading. Kaspersky says some affected sites started temporary mitigations after customer complaints: removing the QR Code and showing only the Pix key (CNPJ), asking buyers to send manual proof of payment, adding the real beneficiary data below the code, or moving checkout to third-party payment intermediaries.
For high-risk merchants and their payment providers, the operational lesson is simple: if the checkout page can be altered, the payment method can be altered with it. The weak point here is not Pix as such, but the merchant-side page and the controls around it.
Related news
All news →
Lula’s possible betting ban in Brazil could cost operators R$ 2.5 billion in licence fees
Brazil’s betting regulation is missing its target: enforcement, hypocrisy, and the real pain point for the sector
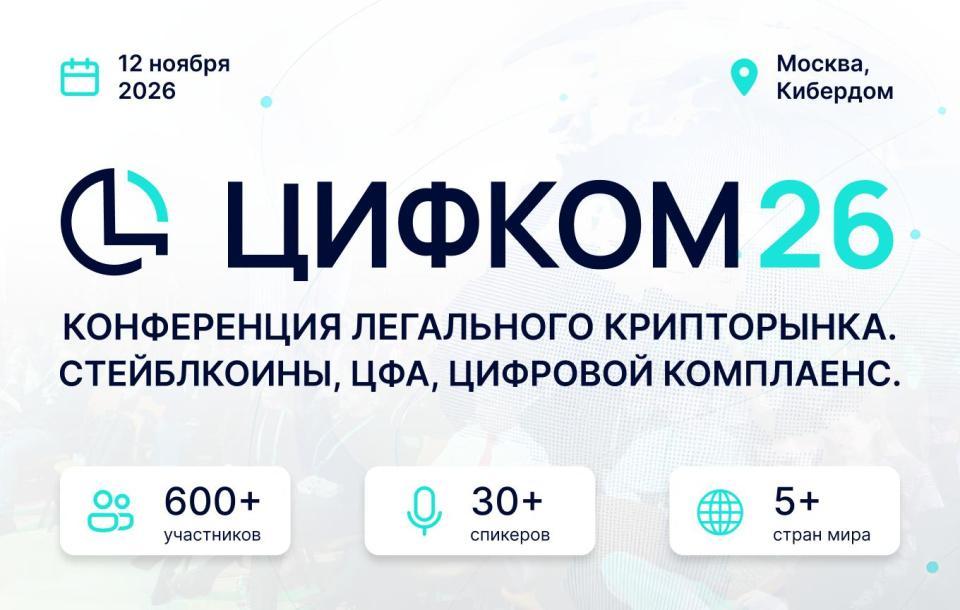
Moscow’s CIFCOM26 will put legal crypto markets, AML/KYC, and cross-border payments on the table on November 12, 2026
Weekly high-risk digest
Regulation, sanctions and payment news across your verticals — once a week, free.
Please check your inbox and click the link to confirm your subscription.
Please enter a valid email address!