Ronald Spektor sentenced to 4 to 12 years in Brooklyn for $15.944M Coinbase phishing scheme
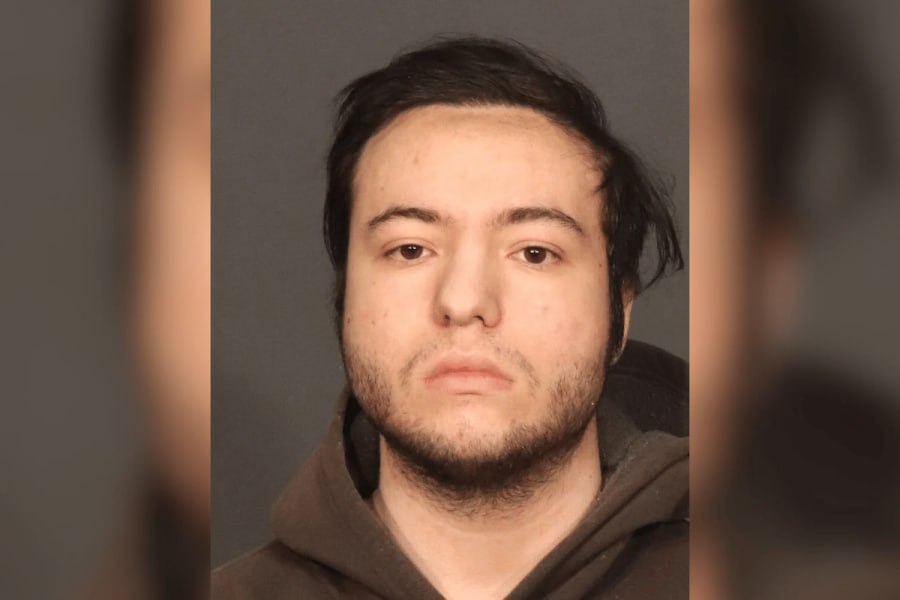
Ronald Spektor, 23, of Sheepshead Bay, Brooklyn, was sentenced on September 23, 2026, to four to 12 years in prison after pleading guilty to a Coinbase phishing and social engineering case that prosecutors said stole roughly $15.944M from about 100 users. For PSPs and crypto platforms, the part that matters is not a technical breach: this was an urgency-driven impersonation scheme that abused user trust and support workflows.
- Brooklyn Supreme Court Justice Danny Chun handed down the sentence after Spektor pleaded guilty on September 2, 2026, to the full 31-count indictment. The plea covered first-degree grand larceny, first-degree money laundering, first-degree criminal possession of stolen property and related counts.
- Prosecutors said Spektor was the organizer of a Coinbase phishing operation that relied on social engineering. Victims were contacted by someone claiming to be a Coinbase representative and warned that a hacker had compromised their accounts, then pushed to move cryptocurrency into wallets they believed they still controlled.
- That is the core mechanic here: no alleged compromise of Coinbase’s systems, just a scam built around account panic and hurried self-transfer instructions. In other words, the weak point was the customer-facing workflow, not the ledger.
- More than 70 of the roughly 100 identified victims were interviewed during the investigation. Reported losses ranged from a California resident who lost more than $1M to a Virginia resident who lost more than $900,000, plus a Pennsylvania victim at about $53,150 and a Maryland victim at about $38,750.
- Prosecutors had sought seven to 21 years and objected to the negotiated term, according to the Brooklyn District Attorney’s Office. The case took about a year to build, which is a useful reminder for fraud teams: these cases are often assembled from complaints, interviews, and tracing, not from one dramatic breach event.
For high-risk operators, the operational takeaway is straightforward: scams like this sit at the intersection of customer support impersonation, withdrawal urgency, and wallet-transfer confusion. If a payment or crypto flow can be redirected by a fake support contact, the fraud surface is already there.
Related news
All news →
Piracicaba bans betting ads in public spaces and events, with rule taking effect in 90 days
Visa and Mesh partner to let crypto wallets spend at 175 million merchant locations
Bank of Russia moves against USDT-to-cash arbitrage as banks start blocking transfers to Belarusian crypto exchanges
Weekly high-risk digest
Regulation, sanctions and payment news across your verticals — once a week, free.
Please check your inbox and click the link to confirm your subscription.
Please enter a valid email address!